Harare, Zimbabwe

Licensed.Protected.Trained.

Data protection, IT support, ICT projects and staff training for Zimbabwean organisations. One team. Fixed fees.

LicenceData controllers must be licensed with POTRAZSI 155 of 2024
DPOA trained Data Protection Officer must be appointedSI 155 of 2024
24 hrsto notify POTRAZ after discovering a breachCyber and Data Protection Act
PenaltiesFines and, for the most serious offences, imprisonmentCyber and Data Protection Act

The Act calls all of these personal data

01 Who this is for

Do you keep people’s records? The Act applies to you.

Patients, pupils, customers or staff. On a server or in a cabinet. If you decide how personal information is used, you are a data controller.

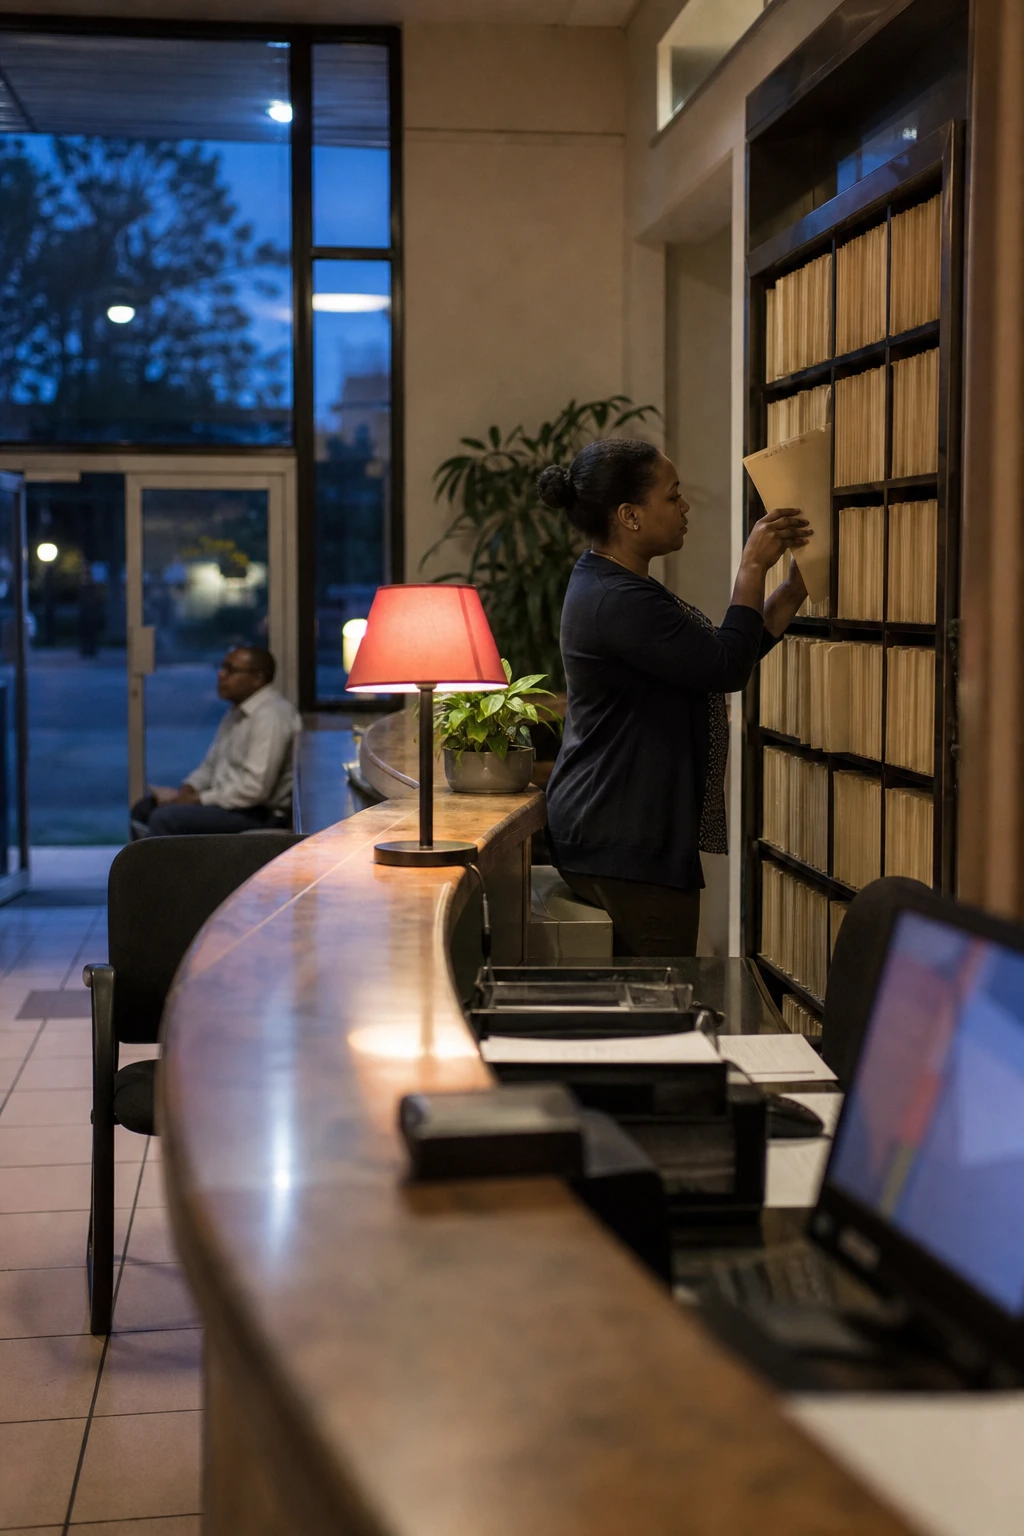
A clinic receptionist filing a patient folder

A wall of patient folders is a database. The Act treats it as one.

Clinics and medical practices

Patient files, test results, ID numbers, next of kin

Health information is sensitive data under the Act and carries the strictest rules of all.

Schools and colleges

Pupil records, parents’ details, fee accounts, photos

Children’s data needs parental consent and extra care, and parents will ask.

Microfinance, SACCOs and insurers

KYC documents, payslips, credit histories, claims

Financial records are what thieves want and what regulators look at first.

Law and accounting firms

Client matters, tax records, contracts, correspondence

Confidentiality is now a statutory duty as well as a professional one.

NGOs and membership bodies

Beneficiary lists, donor records, staff and volunteer files

Donors and partners increasingly ask for proof of compliance before they fund.

Retail, hospitality and property

Loyalty databases, bookings, tenant files, CCTV

A camera pointed at a customer is processing personal data. So is the loyalty card.

02 What the law asks of you

The law asks eight things of you. We help you with every one of them.

The Act set the rules in 2021. SI 155 of 2024 made a licence and a Data Protection Officer mandatory.

  1. 2021

    The Act arrives

    The Cyber and Data Protection Act is gazetted. POTRAZ becomes the Data Protection Authority. Personal information becomes a regulated asset.

  2. 2024

    It gets teeth

    SI 155 of 2024 makes two things mandatory for every data controller: a licence from POTRAZ, and a trained, registered Data Protection Officer.

  3. Now

    Registration, then enforcement

    Licensing and DPO registration are under way across the country. Organisations that can show their paperwork will be fine. Organisations that cannot will be asked why.

You mustThe law saysMazeTech does
01

Get licensed

Register as a data controller with POTRAZ and pay the licence fee for your tier.

We prepare and submit the application, and keep the renewal date.

02

Appoint a DPO

Name a Data Protection Officer who has completed accredited training, and register them with the Authority.

We act as your DPO on a retainer, or prepare the person you nominate.

03

Know what you hold

Keep a record of what personal data you process, why, where it lives and who can see it.

We build the register with you in a day, and it stays yours.

04

Tell people

Publish privacy notices and collect consent where the Act requires it.

Notices and forms in language your customers actually read.

05

Protect it

Take appropriate technical and organisational measures to secure the data.

Tested backups, patched devices, access tied to real people. Our IT service.

06

Report breaches fast

Notify POTRAZ within 24 hours of becoming aware of a breach.

A one-page breach plan on the wall and a number to call.

07

Answer requests

People can ask what you hold, have it corrected, or have it deleted.

A request process, templates and a log, so it takes minutes not weeks.

08

Keep data at home

Sending personal data outside Zimbabwe needs adequate protection or a lawful basis.

We review your cloud tools and vendors and tell you which are fine.

03 Two-minute self-check

Does the Act apply to you, and what do you need first?

Seven questions, two minutes, no email address. You get a straight answer and a list of what to fix first.

  • Whether you are a data controller
  • Whether you hold sensitive data
  • Which of the Act’s basics you are missing
  • What to fix first, and who does it

Question 1 of 7

Do you keep any records about people: customers, patients, pupils, members or staff?

04 What we do

Compliance, IT, projects and training. One team.

If you get them from four suppliers, the gaps between each are where breaches live.

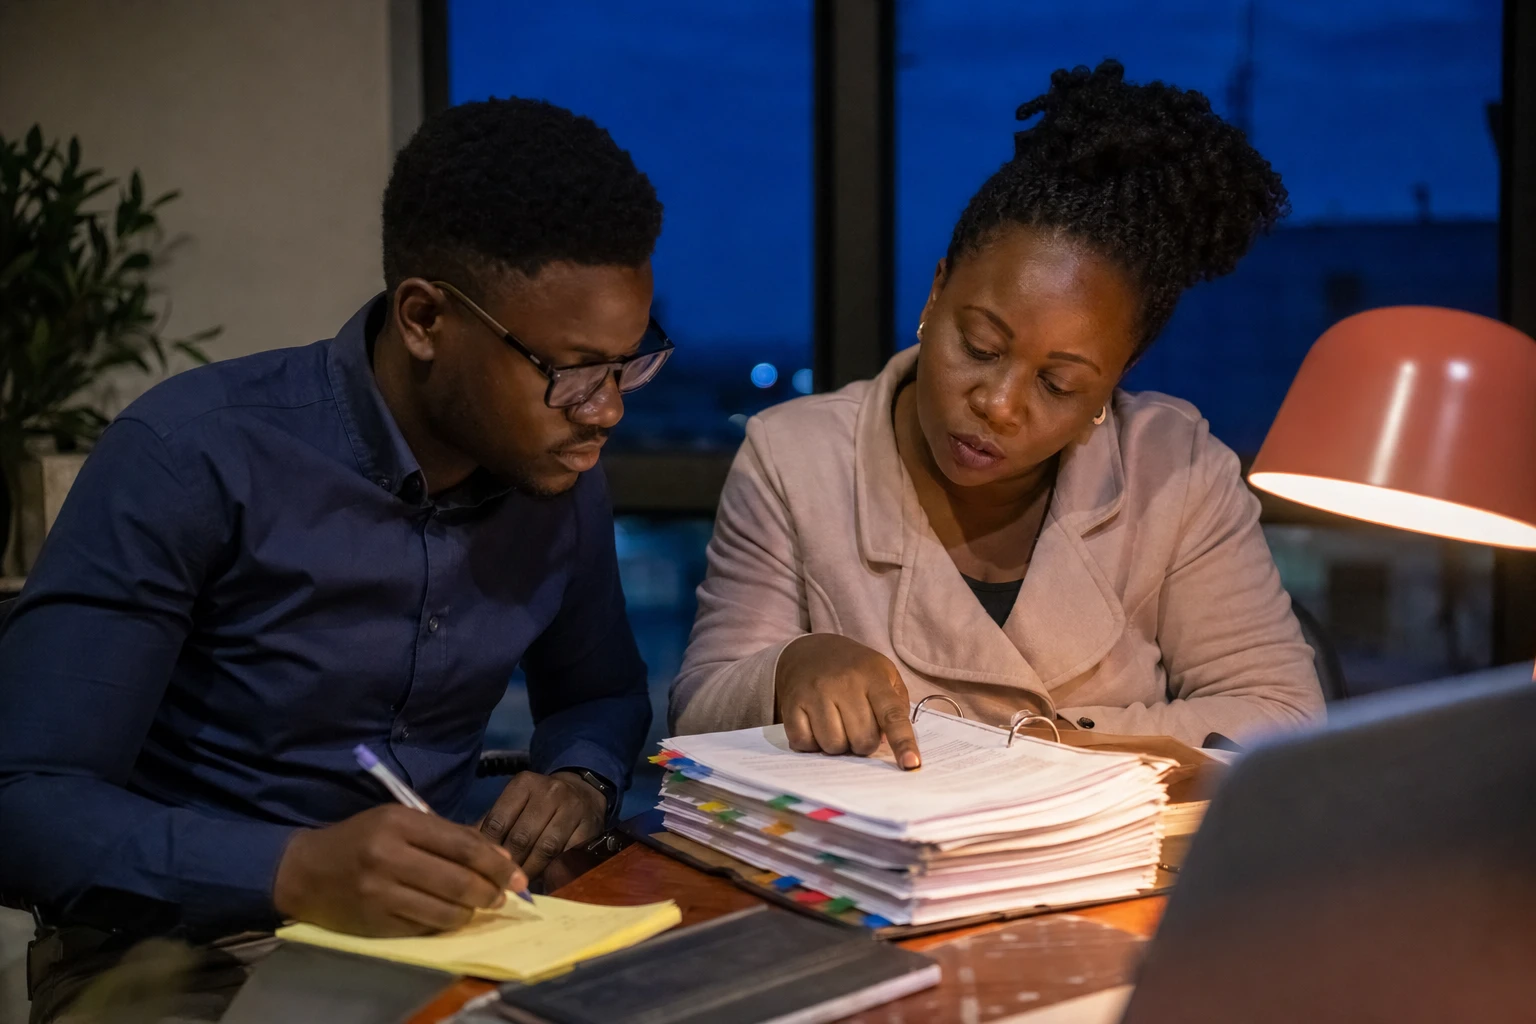
A consultant and an administrator working through a binder of records together 01 / 04

Data Protection & Privacy

Get licensed, appoint your DPO, and show POTRAZ your paperwork when they ask.

  • Gap assessment with a prioritised, costed plan
  • POTRAZ data controller licence application, submitted and tracked
  • Data Protection Officer: outsourced, or your nominee trained and registered
  • A register of what you hold, why, where and who can see it
Everything in data protection & privacy
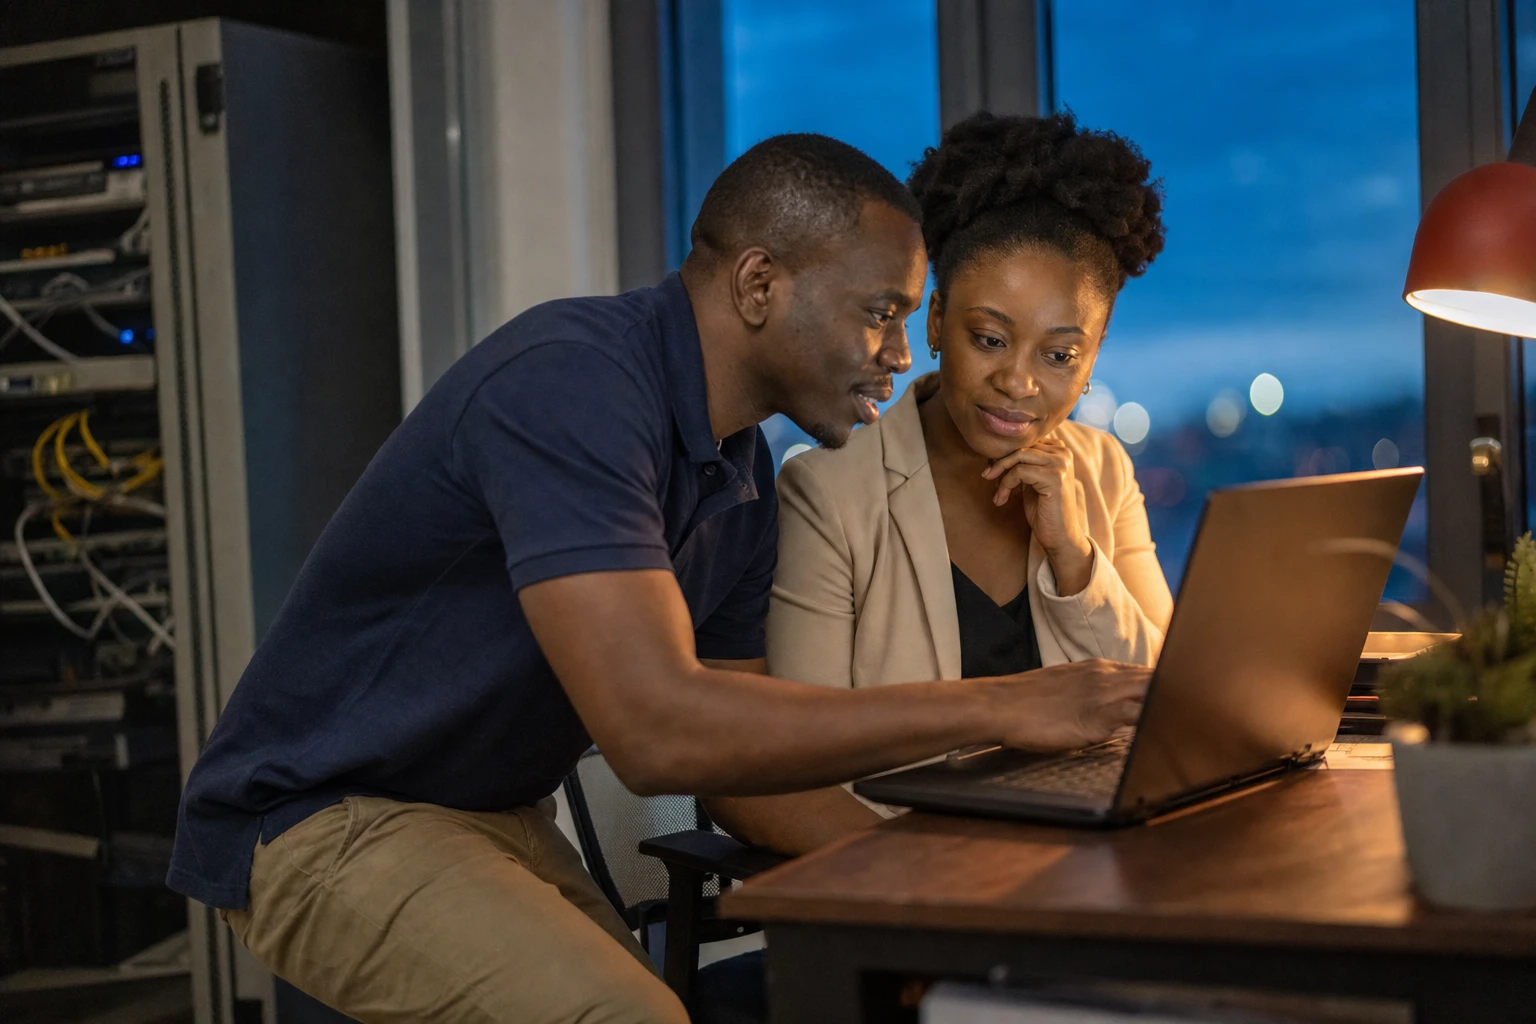
An IT engineer fixing a laptop at an employee’s desk 02 / 04

Technical Support

The IT department you can’t justify hiring, with the Act’s security built in.

  • Remote and on-site helpdesk with a named engineer and agreed response times
  • Backups set up, tested monthly, and restored when you need them
  • Devices patched, protected and set up securely; old ones wiped properly
  • Office Wi-Fi, network and internet failover that survives load-shedding
Everything in technical support
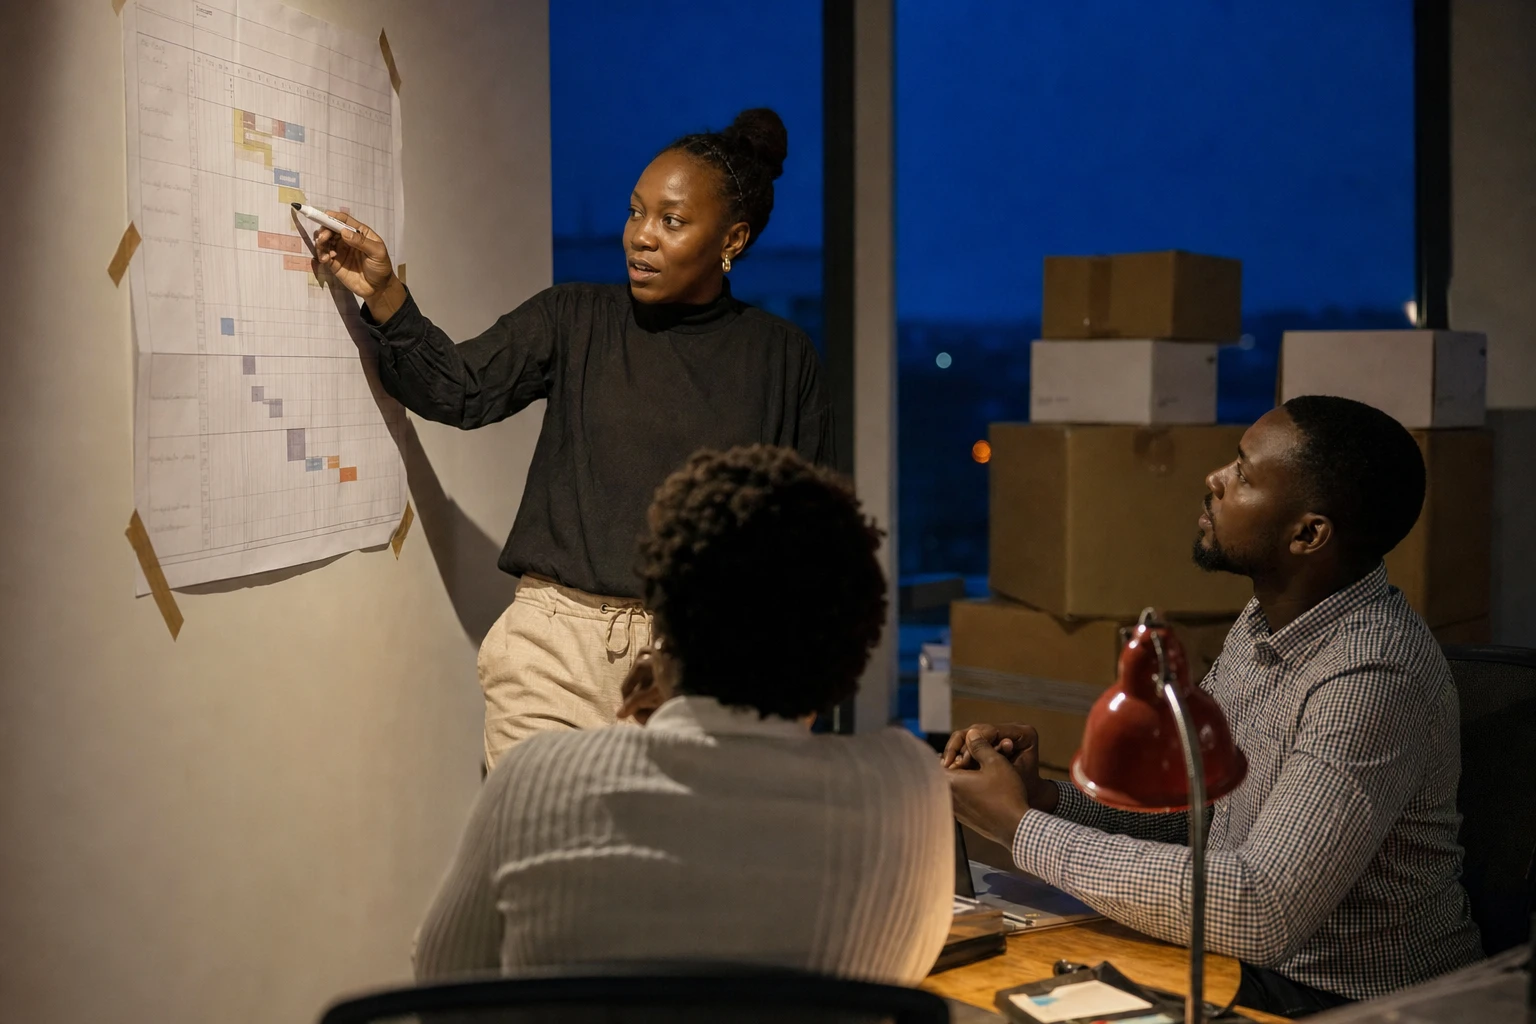
A project manager walking colleagues through a schedule on the wall 03 / 04

Project Management

ICT projects delivered on time, on budget, and properly handed over.

  • A written plan with dates, owners and a budget
  • One point of contact for every supplier and vendor
  • Quotes compared and contracts read before you sign
  • A weekly progress note in plain English
Everything in project management
A trainer at a whiteboard with a small group of staff 04 / 04

ICT Training & Support

Two hours turns your staff into the first line of defence.

  • All-staff data protection awareness, two to three hours
  • Data Protection Officer preparation programme
  • Cyber hygiene: passwords, phishing, devices and public Wi-Fi
  • Microsoft 365 and Google Workspace, used properly
Everything in training

05 Your first 30 days

From the first call to compliant, in thirty days.

Every engagement starts the same way, so the price and the timeline are settled before you commit to anything.

  1. Day 1

    A 20-minute call

    Tell us what you hold and what is worrying you. We tell you whether the Act applies, what it will take, and roughly what it costs. No charge.

  2. Week 1

    Gap assessment

    On site or remote. We walk your systems and paperwork with you: what data, where, who has access, what is missing.

  3. Day 10

    Written report

    Every gap, its priority, and a fixed price to close it. The report is yours whether or not you continue.

  4. Weeks 2 to 4

    Build

    Licence application, DPO, register, notices, breach plan, and the IT fixes that the assessment flagged.

  5. Month 2 on

    Embed

    Staff training, DPO handover or retainer, quarterly reviews. Compliance that holds next year, not just this quarter.

06 What you can hold us to

Six promises. All of them in writing.

A fixed price before work starts. A named person who answers the phone. A date on every deliverable. None of that is a slogan; all of it goes in your engagement letter.

Fixed fees, in writing

You get a price before work starts, and the price does not move unless the scope does.

A named person

The engineer who set up your backups is the one who answers when something fails. Not a queue.

Plain language

A policy your receptionist can follow beats a forty-page PDF nobody has opened. We write the first kind.

Built for here

Load-shedding, patchy bandwidth and USD budgets are inputs to the design, not excuses afterwards.

One team, not four suppliers

The policy, the laptop, the rollout and the person using it all agree, because the same people did all four.

Lawyers where lawyers belong

We do compliance, IT and training. When a question needs a legal opinion we say so, and we work alongside your lawyer.

07 Questions

What people ask on the first call.

Not here? Ask. The first call is free.

We have five staff. Does the Act really apply to us?

Yes. The obligations attach to anyone who decides why and how personal data is used, not to a size of organisation. If you keep records about customers, patients, pupils, members or employees, you are a data controller.

What happens if we just ignore it?

The Act provides for fines and, for the most serious offences, imprisonment, and POTRAZ can inspect and enforce. In practice the first pressure often comes sooner and softer: a donor, a tender, an insurer or a bank asking for proof of compliance you cannot produce.

What does it cost?

It depends on what you hold and what is already in place, which is why we start with a fixed-fee gap assessment and a written, costed plan. You will know the full price before any further work begins.

Do we have to hire a Data Protection Officer?

You have to appoint one. That can be an existing staff member who completes accredited training, or MazeTech acting as your DPO on a retainer. We help you decide which is right for your size.

Do you work outside Harare?

Yes. Assessments, DPO services and most IT support run remotely; we travel for on-site work. Ask us about your location.

Is this legal advice?

No. MazeTech provides compliance, IT and training services. Where a question needs a legal opinion, we say so and work alongside your lawyer.

08 Start

Twenty minutes is enough to know where you stand.

Tell us what you hold. We tell you whether the Act applies, what it takes, and roughly what it costs. No charge.

Prefer to write it down? Send us a message and we will call you back.